
Cyber Risk Doesn’t Arrive, It Accumulates
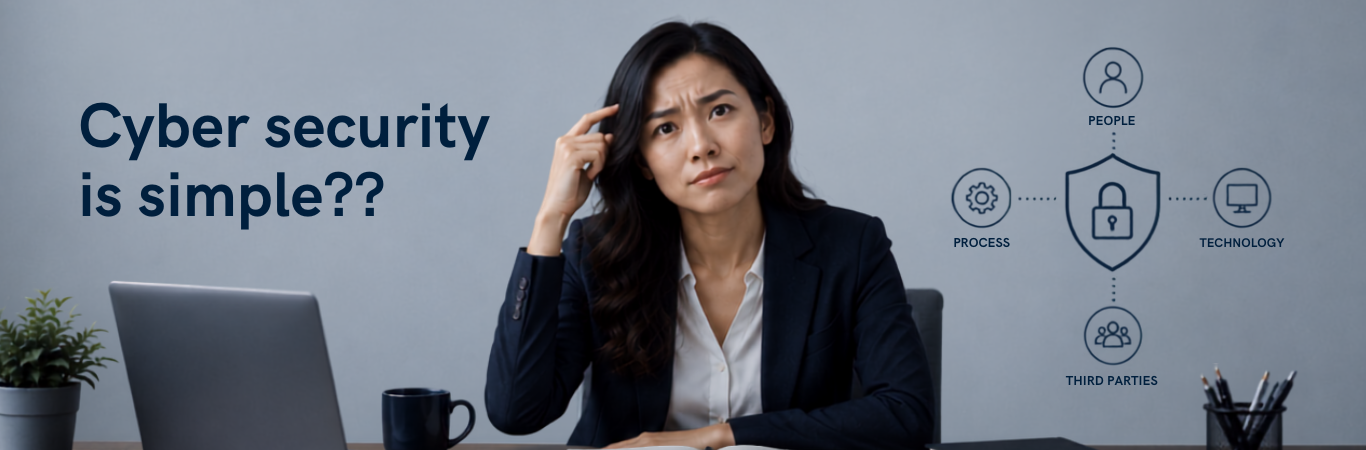
Most cyber incidents don’t start with a dramatic, sophisticated attack. They build quietly, over time, through small everyday decisions that seem perfectly reasonable in the moment.
That was the crux of our recent Cyber Conversations webinar, When Small Oversights Result in Big Cyber Problems, where our Managing Director Robert Buck and Business Technology Consultant Team Lead Gavin Hall unpacked how risk actually develops inside an organisation and why it so often stays invisible until it’s too late.
Is cyber security simple?
Rob opened with a deliberately provocative question: is cyber security simple?
His answer, it’s simple in the same way spinning plates is simple. The individual idea is easy to grasp, but keeping every plate spinning at once is where it gets hard.
“Cyber security is a team sport. Everyone has a role — from the end user who’s hopefully not clicking on a phishing email, through to the highly technical person. But if there’s too many plates to watch, that’s when things go wrong” said Rob.
When a major breach hits the headlines, the word we always hear is sophisticated. Yet the reality is usually far more mundane. Rob pointed to Medibank, one of Australia’s most publicised breaches, which traced back to a chain of very simple oversights:
- Credentials saved in a browser and synced to a personal home computer
- That home device was already infected with malware
- The compromised login held near-total administrative access
- The corporate VPN had no multi-factor authentication (MFA)
- Security alerts fired, but no one acted on them
Four plates dropped at once. The result: close to 10 million customers had personal information stolen and sold on the dark web, more than $100 million spent on cleanup and rebuild and significant additional capital reserves imposed by the regulator.
“What were fairly simple mistakes from a cyber point of view had an absolutely enormous impact” added Rob.
The fixes are equally fundamental: use a password manager with an encrypted vault rather than the browser, restrict admin privileges (a core control in the Essential Eight), put MFA on everything, especially remote access and never assume someone is watching your security alerts.
Where risk actually forms
Gavin then shifted the lens from how breaches happen to where the risk quietly accumulates and made the point that risk doesn’t sit neatly in one box labelled “IT.”
“It forms across people, process, technology and, increasingly, third parties. Most of the time it’s not highly visible, it’s building gradually through normal, reasonable decisions that don’t stand out on their own,” stated Gavin.
He walked through four patterns Diamond IT sees again and again:
1. Access that only ever grows
Picture a new starter holding a single “plate” of access on day one. Over time they change roles, pick up responsibilities, help another team and each time, they’re handed another plate. We assume someone reviews and takes plates back when roles change. In practice, that rarely happens in a structured way. Worse, the next new hire often inherits someone’s entire access profile (“just give Michael everything Stacey has”) and starts on day one holding ten plates, not one. Ask yourself: could you say, today, who has access to what across all your systems?
2. Ownership that falls into the gap
Who owns access reviews? Who owns vendor risk? Who owns the data in your systems? At a high level, most organisations say “we’ve got that covered.” Follow it through, though and IT assumes the business owns the decision while the business assumes IT is handling the technical side. No one made a bad call but shared responsibility doesn’t equal clear ownership and things slip into the space between teams.
3. Third parties you rely on more than you realise
Cloud platforms, SaaS tools, outsourced providers, all reasonable, all helping you move faster. But they’re not outside your environment; they hold your data and connect to your systems. Few organisations can quickly answer which third parties have access to our sensitive data? Especially when those providers rely on their own third parties, creating a fragile supply chain and a risk footprint far larger than expected.
4. The illusion of “we’re fine”
Day to day, nothing looks broken, systems work, people get their jobs done. Which is exactly why it’s a shock when risk suddenly surfaces through an incident, a near miss, an audit finding, or a leadership question. By then, the risk hasn’t appeared, it’s been building all along across access, ownership and dependencies that never neatly connected.
A real-world example
To make it concrete, Gavin shared the case of an Australian fixed-income investment firm that suffered a cyber incident in 2023, a case now documented publicly through the Federal Court.
The entry point was simple: an employee unintentionally downloaded a malicious file. The attacker gained access, moved laterally through the environment and ultimately extracted just shy of 400GB of data, affecting 18,000 people’s sensitive personal and financial records. Tellingly, the firm didn’t detect it internally, they were alerted by an external party.
What followed mattered most. The regulator (ASIC) acted not simply because a breach occurred, but because of how cyber risk had been managed over the lead-up. The court found failures across multiple areas, resulting in a $2.5 million penalty plus the regulator’s legal costs.
“The challenge isn’t that something suddenly went wrong. It’s that there wasn’t clear visibility early enough to influence it along the way,” added Gavin.
The conversations worth having
The takeaway wasn’t “buy more tools.” As Gavin put it, there are more tools available than ever — what’s usually missing is clarity. The questions leaders rarely stop to ask together:
- What information actually matters when it comes to understanding our cyber risk?
- Who owns the decisions, not technically, but at a leadership level? Who can say yes, no, or not yet?
- What happens if something goes wrong tomorrow, in practice, not in theory?
- Where are we exposed through others we depend on?
- And the hardest one: what are we choosing not to address?
“It’s not about fixing everything. It’s about understanding enough to make better decisions,” affirmed Gavin
Reframing cyber as a business issue
Cyber security isn’t purely an IT problem to be delegated and forgotten, it’s a business issue, underpinned by governance, controls and risk management. The plates only stay spinning when someone, at a leadership level, is accountable for keeping an eye on them.
Watch the Webinar Here 👉 When Small Oversights Result in Big Cyber Problems
How Diamond IT can help
We help organisations across all three dimensions of cyber, protecting against attack, detecting and responding when something gets through and putting the governance and risk controls in place to keep it all under control.
For many businesses, the best first step is our Cyber Risk Discovery, a deliberately accessible way to look at cyber from a business risk perspective: how you use data, where your real exposure sits and what to prioritise, in the right order.
If something in this struck a chord, let’s have the conversation before an incident forces it.
Reach out to our team via email at enquiries@diamondit.com.au, call 1300 307 907 or fill out the form below.
